 Politics & Law
Construction ministry proposes investment in equipment to counter illegal UAVs near airports
1.
|
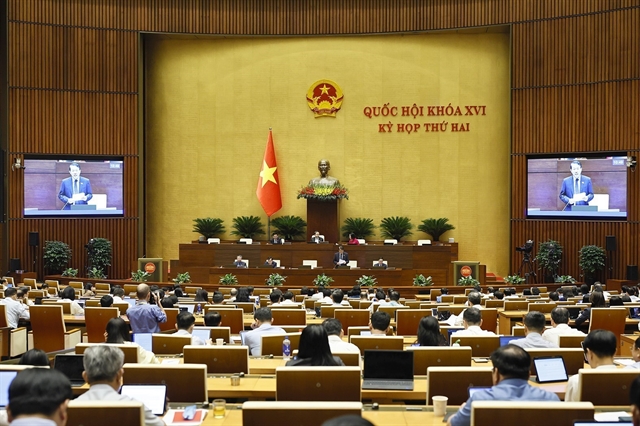
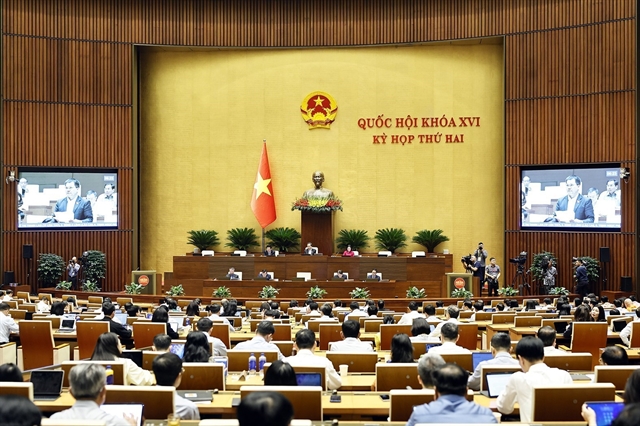
| General Lương Tam Quang, Minister of Public Security, explains to the National Assembly the draft Law on Electronic Identification and Authentication and the draft Law on Data Security. VNA/VNS Photo |
HÀ NỘI – The expansion of electronic identification must be accompanied by minimal data collection and privacy safeguards, while data security obligations should be proportionate to risk to avoid imposing unnecessary compliance burdens on businesses, said General Lương Tam Quang, Minister of Public Security. rissk
The minister highlighted a number of issues arising as electronic identification becomes more widespread, while explaining and responding to National Assembly (NA) deputies' comments on the draft Law on Electronic Identification and Authentication and the draft Law on Data Security at yesterday's session.
Issues under the spotlight included regulating the collection and use of data to prevent violations of privacy and the classification of data security risks to protect critical sectors while reducing administrative burdens on businesses.
Regarding the draft Law on Electronic Identification and Authentication, key issues include the automatic creation of digital identities, the principle of minimum data collection, privacy protection and requirements to link electronic transaction accounts with national electronic identities in high-risk sectors.
The draft Law on Data Security focuses on a five-tier risk classification mechanism, the division of management responsibilities between the Ministry of Public Security and the Ministry of National Defence and regulations on security cryptography and post-quantum cryptography.
Minimum data collection, privacy protection
Regarding the scope of electronic identification, General Quang said that Article 7 of the draft law identifies the groups of entities eligible for electronic identification.
Article 8 specifies the groups to be identified by State agencies, including agencies, organisations, individuals, locations, spaces and entities whose information falls under core or important data; entities certified as owning or using high-risk products and goods; and entities involving State secrets.
The Government will also be tasked with issuing a list of entities subject to State-led identification and setting out an implementation roadmap, ensuring that the regulations are suited to the country's practical digital transformation conditions.
Regarding automatic identity creation, the draft law stipulates that where the information required to establish an electronic identity is already complete and accurate in national or specialised databases, State agencies will automatically create the electronic identity and issue a national identification code for the entities specified in Clause 1, Article 8.
For privacy protection, the minister emphasised the principle of collecting only the minimum necessary data and ensuring that the synchronisation of identification and authentication data is subject to safeguards.
"The draft law has designed multiple layers of privacy protection," the minister added.
"The collection of minimum data must have the consent of the data subject; transaction content must not be synchronised; and authentication results must not be shared beyond the permitted scope."
Personal data processed in electronic identification and authentication activities will continue to be strictly protected under personal data protection legislation. The principles, conditions, scope and purposes of personal data processing will remain unchanged.
Electronic identification and authentication must comply with the Constitution and the law, safeguarding the rights and interests of agencies, organisations and individuals. The use and exploitation of electronic identities must ensure information confidentiality and comply with personal data protection regulations.
Phạm Trọng Nhân, a deputy from HCM City, highlighted the limitations of relying on biometrics, given the rapid advancement of spoofing technologies.
According to the deputy, while biometrics remain necessary, they cannot be considered the sole solution for preventing fraud.
“Users have long assumed that features such as faces, voices, and fingerprints are the most difficult to forge; however, the development of AI has rendered this assumption no longer sufficiently secure,” he said.
Sharing concerns regarding the risks posed by authentication technologies and artificial intelligence (AI), deputy Tô Ái Vang from Cần Thơ City argued that the draft law should clearly define the responsibilities of AI solution providers in cases where their systems produce incorrect authentication results.
She said that under the current proposal, organisations or individuals utilising identification and authentication results from an AI system would bear ultimate responsibility for any decisions made based on those results.
“However, this approach fails to fully capture the nature of the accountability relationship between the end-user and the party that develops or provides the technology,” she said.
Risk-based classification and reduced compliance burdens
Regarding the draft Law on Data Security, Quang said that risk classification was a cornerstone of the proposed legislation, as it would enable authorities to assess the potential harm caused by data breaches and impose corresponding protection obligations.
"Regarding data security risk levels, the risk classification mechanism is a cornerstone of the draft law," the minister added.
"Only by correctly identifying the level of harm that could result from data breaches can we impose proportionate obligations, avoiding both excessive protection requirements in low-risk areas and inadequate protection in high-risk areas."
Following the conclusions of the NA Standing Committee, the draft law establishes five risk levels corresponding to the five levels of information systems under the Law on Cybersecurity.
Notably, Clause 4, Article 8 allows organisations to use risk classification results already obtained under cybersecurity legislation, preventing the same information system from having to undergo two separate assessments.
Risk classification will neither replace the classification of core and important data under the Law on Data nor create a new list of data categories. Instead, it will serve as a basis for selecting appropriate protection measures.
Concluding his explanation, Quang said that the drafting agency would work closely with the Standing Committee of the National Assembly's Committee on National Defence, Security and External Relations to fully incorporate deputies' comments and report to the National Assembly Standing Committee before finalising the draft laws. VNS
Loading rewrite
Politics & Law
 Politics & Law
 Politics & Law
 Politics & Law
 Politics & Law
 Politics & Law
 Politics & Law
 Politics & Law
 Politics & Law
 Politics & Law
 Politics & Law
 Politics & Law
 Politics & Law
 Politics & Law